





ensor is a fast, interactive CLI tool for detecting and redacting secrets from your codebase and managing environment variable configurations — ensuring leaked API keys, tokens, and credentials never make it into a commit, screenshot, or public release.
By default, ensor extracts discovered secrets into a .env file and substitutes them with customizable placeholders across your project, but also includes a versatile converter for .env, JSON, YAML, and TOML.
- 🔍 Secret scanning & redaction — walks all files and directories and redacts secrets automatically
- 🔄 Format conversion — convert between
.env, JSON, YAML, TOML, and more - 📁 Smart skipping — dot-prefixed files like
.envand.git/*are ignored by default - 🎨 Beautiful TUI — interactive prompts built with huh and bubbletea
- ⚡ Zero config — no config files, no setup. Just run it.
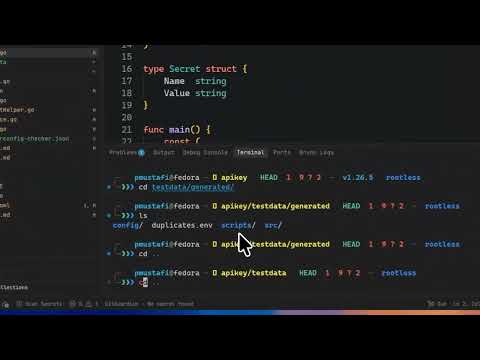
Watch ensor in action:
mise use github:pratyay360/ensor@latestcurl -sSL https://raw.githubusercontent.com/Pratyay360/ensor/main/install.sh | shgo install github.com/Pratyay360/ensor@latestDownload ready-to-run binaries or .deb, .rpm, and .apk packages from the Releases page for Linux, macOS, Windows, and FreeBSD.
Scan the current directory:
ensorThat's it. ensor walks all the files and directories in your project and redacts the secrets from them.
By default, ensor skips scanning any file or directory that starts with a trailing dot, like .env, .env.json, or .git/* — so your actual secret files stay untouched.
Run
ensor --helpto see all available options.
ensor convert converts between any format of env files. Convert .env, YAML, TOML, JSON, and more — interchangeably.
ensor in action

ensor convert

Contributions are always welcome! Feel free to open an issue or submit a pull request.
Licensed under the Apache-2.0 license.
Special thanks to these amazing open-source projects:
- betterleaks — High-performance secret detection engine
- huh — Interactive prompt and form toolkit
- bubbletea — Terminal UI runtime
- lipgloss — Style definitions for terminal applications